
 CLICK HERE TO DOWNLOAD THIS IMAGE & COLOR IT IN!
Inside: Boston Scientific’s two-week cyber siege becomes fuel for our incoming Scenario Library, fresh breach chronicles with a variety of attack paths, and a powerful new way to end each TTX you deliver with Ally.

Boston Scientific has been under cyber siege for more than two weeks. The assault began on August 25th, landing critical hits across manufacturing, distribution, and operations applications. Despite immediately calling upon its IRP and IR retainer, the kingdom’s operations came to a grinding halt by the end of week one.
As of today (September 15th), the source of the siege remains concealed. Operations were finally restored this past Wednesday (September 9th), but Boston Scientific now has three powerful bosses to face: a backlog of delayed orders, lingering financial damage, and the unsolved mystery of how this all began.
Following the first two weeks of battle, the kingdom revised its initial 8-K filing with the SEC under section 8.01, “Other Events,” to a filing under section 1.05, “Material Cyber Incidents,” just yesterday. This marks the point where the siege dealt material business impact, with Boston Scientific now expecting the disruption to weigh on sales and earnings.
Takeaway: This is exactly the type of incident organizations should be practicing, and Ally is here to lend aid. We’ll soon be unveiling our Scenario Library, an archive of pre-built templates inspired by real-world incidents.
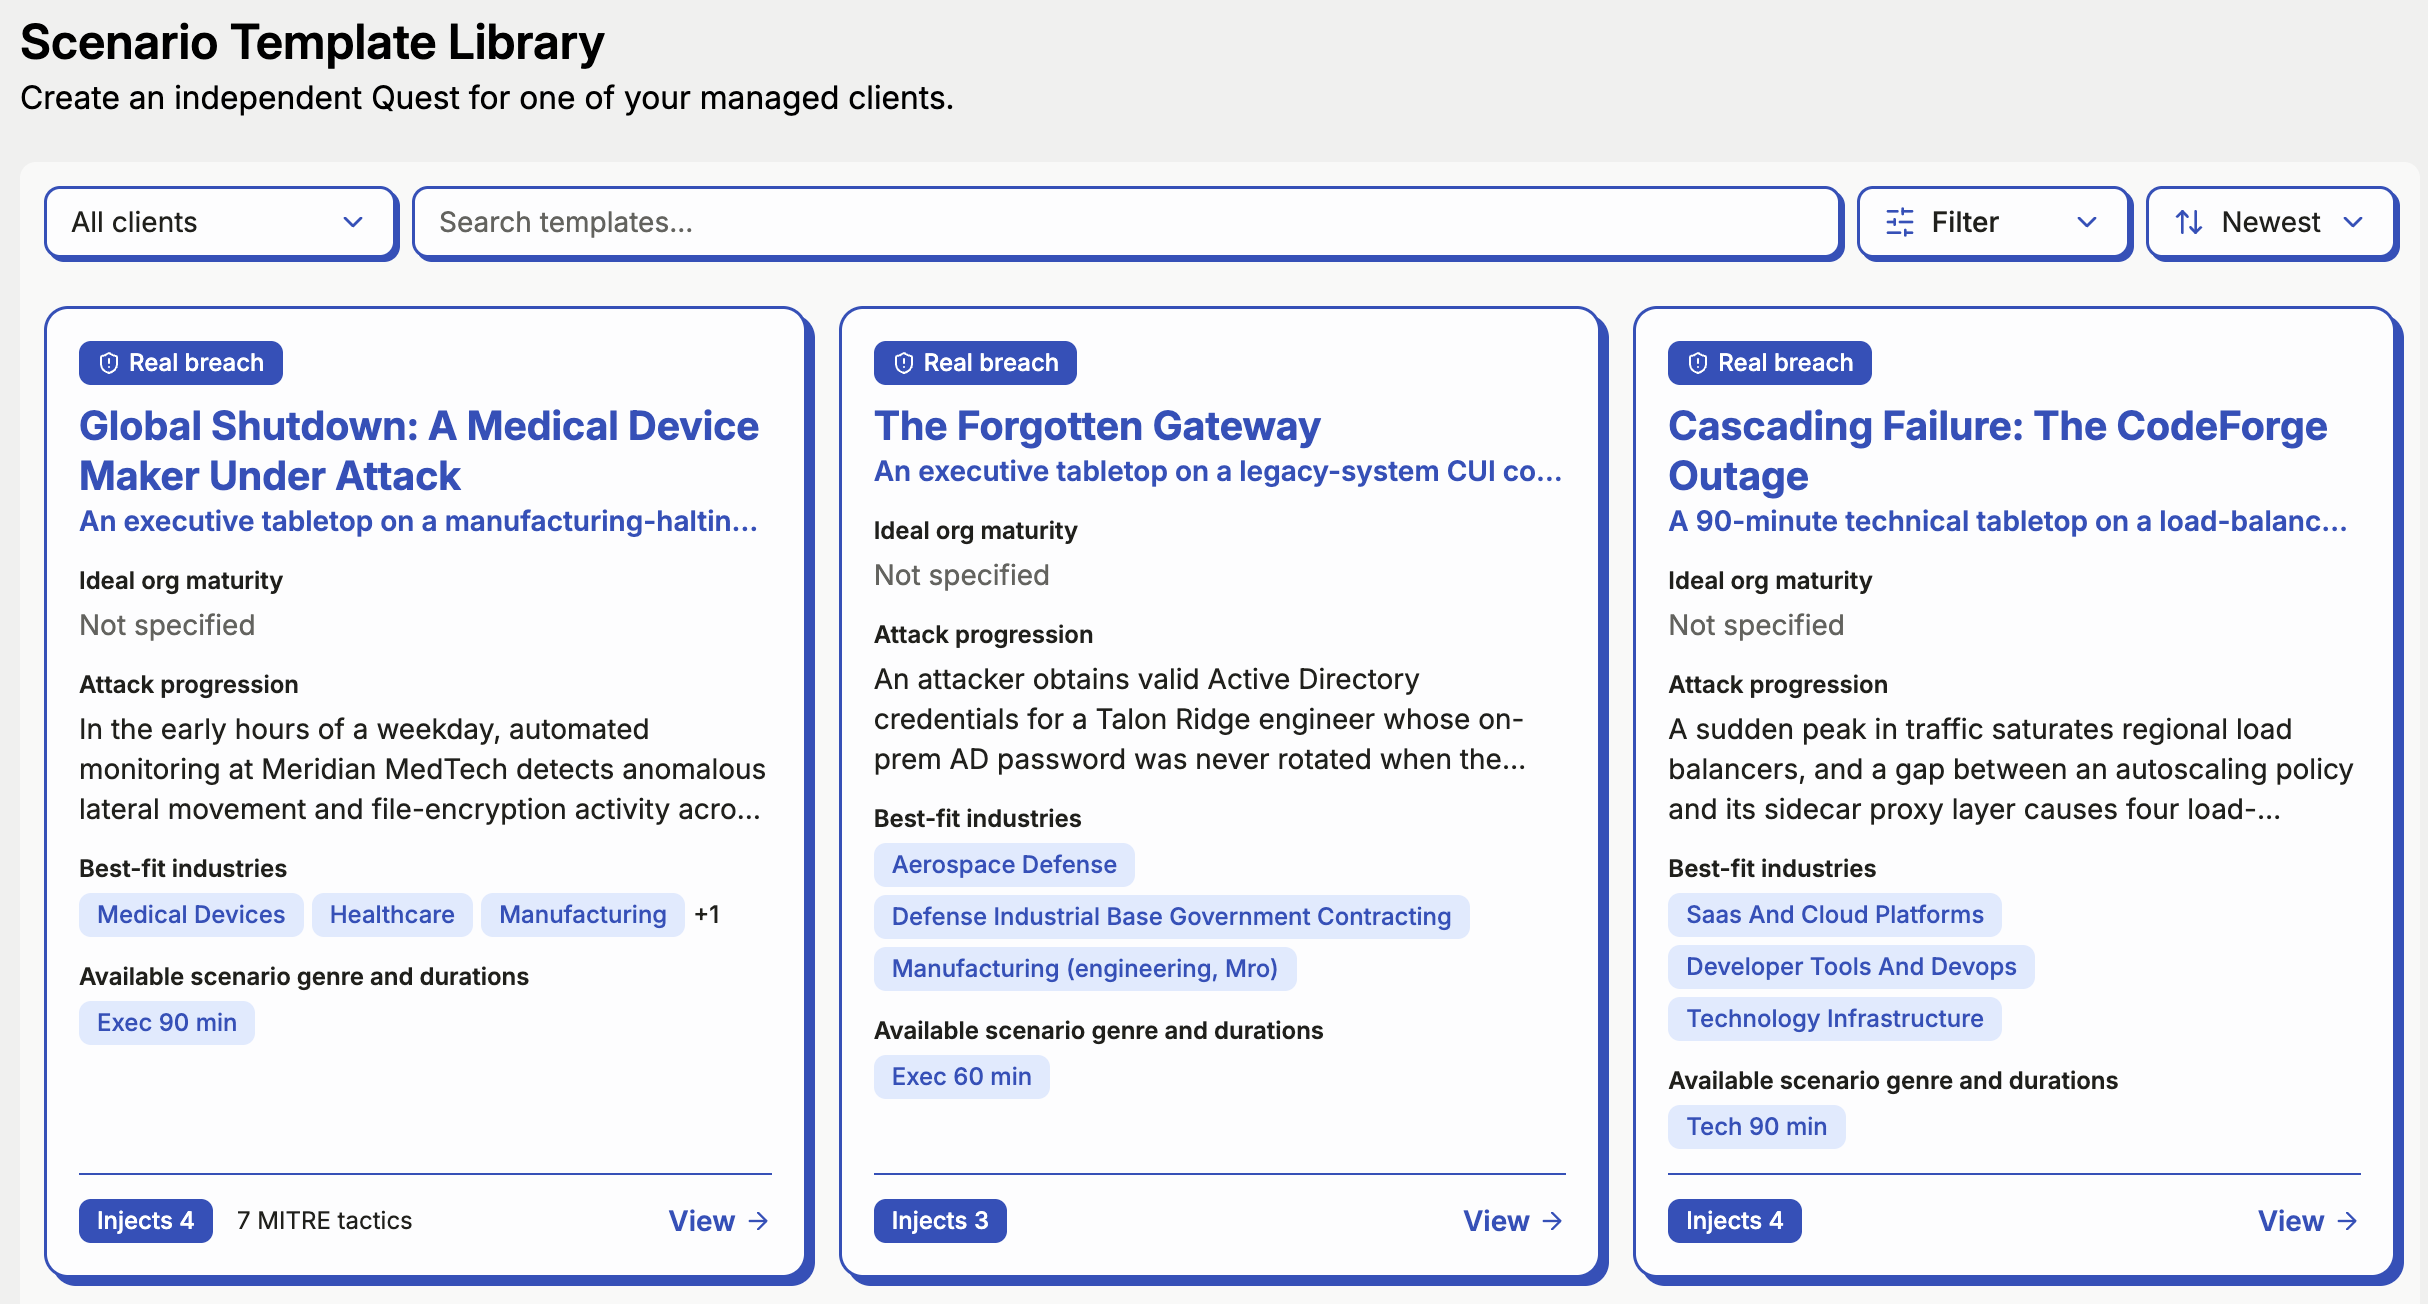
A template has already been crafted based on the battle at Boston Scientific, challenging party members with questions like:
We won’t know the full toll of this siege for months (or maybe years), but you can practice this type of incident today. If you’re interested in testing Scenario Library templates like this one, please send us an email.
Your allies in IR,
Rob & Scout
The cyber siege at Boston Scientific has caused lingering damage. Even as systems are healed, the fallout has thrown its 2026 outlook off course. A scenario like this can test whether the party’s recovery plan extends beyond systems restoration. Survey the damage
Notorious bandit gang ShinyHunters claims it talked its way through McKesson’s gates via vishing, then raided Salesforce and Snowflake. Facilitators can use this tale to discover how the party responds when a stolen identity becomes a master key. Examine the report
Manchester Airports Group refused FulcrumSec’s extortion demand, so the brigands unleashed data tied to 8.7 million customers. A scenario like this explores how the party protects the realm when saying “no” to evildoers creates an avalanche of consequences. Study the aftermath
Ransomware raiders breached an ATF system holding sensitive data. Fortunately, the chamber was walled off from the agency’s other systems. This type of scenario can test whether the party can contain an intruder before the breach spreads through the castle. Open the scroll
Crafted by Elvira!
No great quest should end with the party wondering, “Wait, is that it?” To give each TTX a better sense of finality, we’ve forged a new way to close out your sessions.
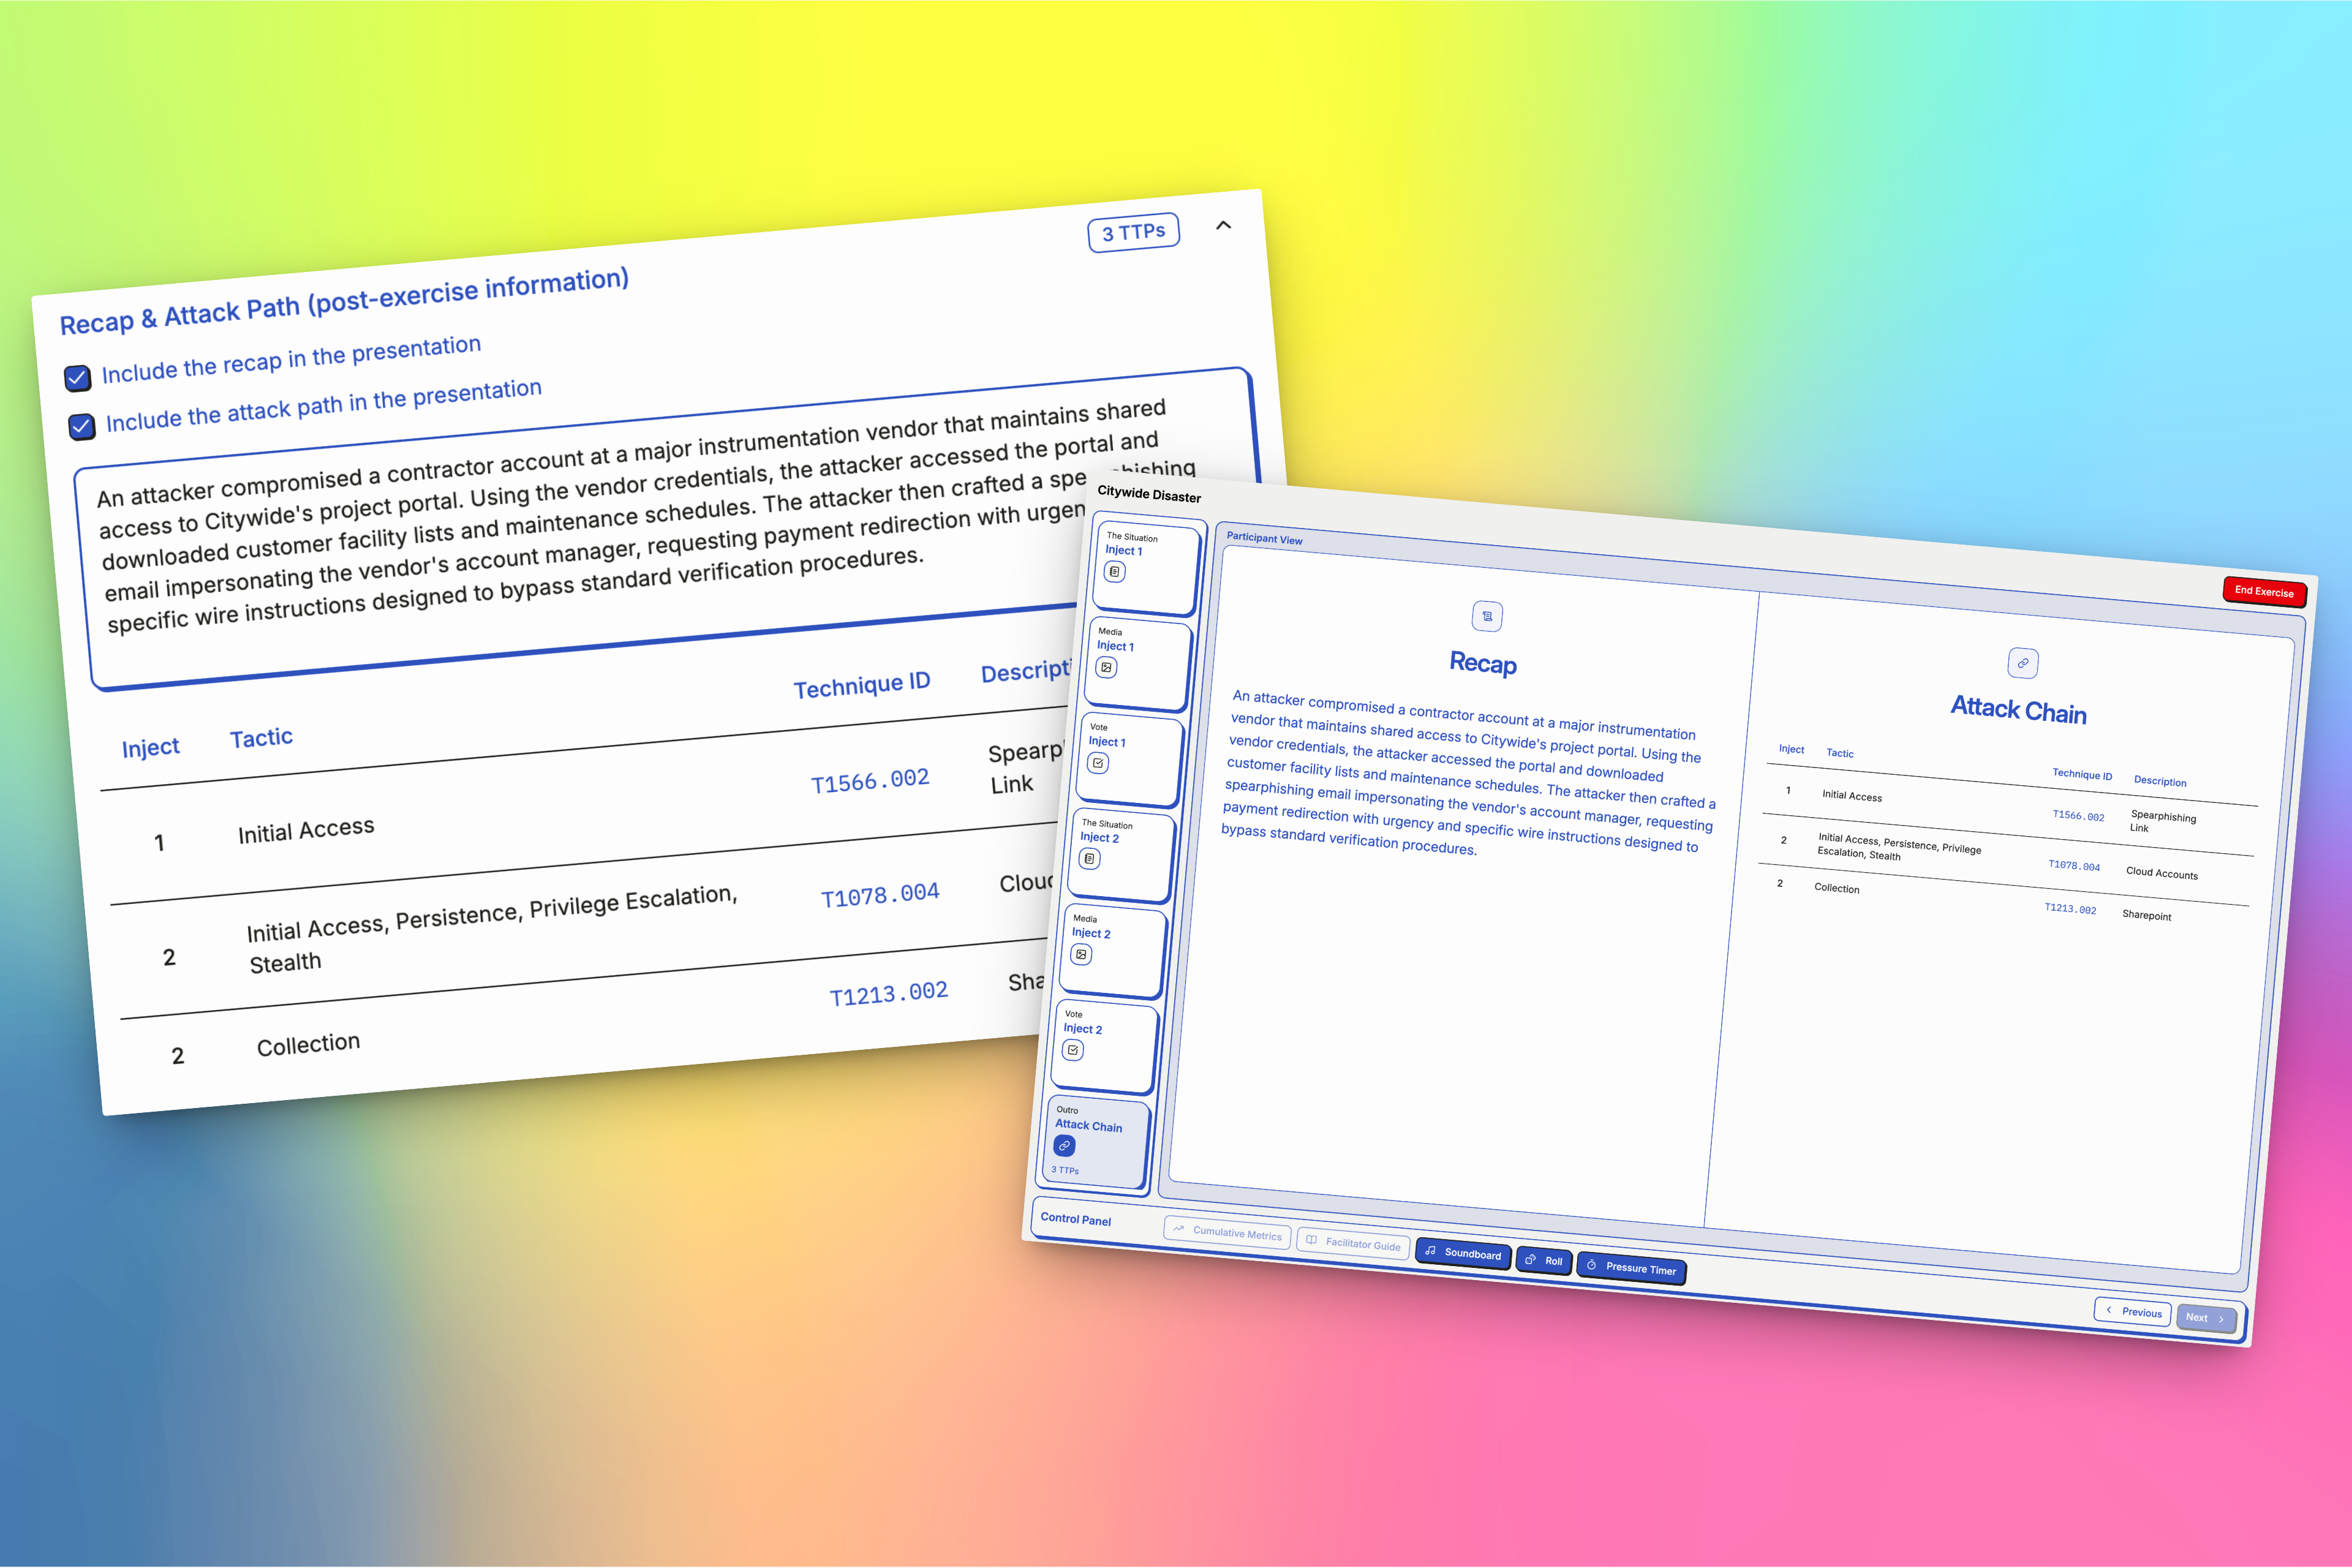
From the Inject Editor, Facilitators can now choose to end a quest with an Exercise Recap, an Attack Path, or both. This gives the exercise a clear conclusion before the hotwash begins.
Together, this pairing of tools gives Facilitators a grand finale before closing the book on a TTX. Create a free account and try it out for yourself.

From a fortnight-long siege at Boston Scientific to a stealthy intrusion by ShinyHunters, this scroll has taken us down a variety of attack paths. May they inspire your next scenario. And on a separate note, we look forward to sharing Ally’s Scenario Library with you soon!
P.S. We’ve got a CMMC-themed chapter of TTX Thursday coming up this week on September 17th. Register here if interested!

About Ally Security
Ally is here to support facilitators, which in turn creates a virtuous cycle where exercises take less time, provide more value, are run more frequently, and can make every organization can be better prepared.
The unexpected wins. The client curveballs. The chaos you couldn’t have scripted if you tried. Dear Asa is your space to share the stories that don’t make it into the official post-incident report. Script, submit, and enjoy a chance to be featured or quoted in an upcoming post.


